Quick answer: A WordPress security plugin is software you install to perform defined security tasks, such as scanning files, limiting login attempts, checking configuration or applying firewall rules. A managed website security service is an ongoing operational arrangement in which a provider uses tools, people and documented procedures to monitor, investigate and, when the contract includes it, respond to security problems. The central difference is not that one is “secure” and the other is “insecure.” It is who owns the work after an alert appears. A well-configured plugin can be enough for some lower-risk sites with a capable owner; a managed service can be more suitable when business impact is high or no one internally can reliably handle security events.
Neither option makes WordPress invulnerable. A service may rely on the same plugins that a business could install itself, while some premium plugins include remote scanning, expert support or cleanup assistance. Labels overlap, so compare actual coverage and contractual responsibilities instead of assuming that “managed” automatically means around-the-clock human response. The official WordPress hardening handbook describes website security as risk reduction rather than a one-time fix.
WordPress security plugin vs. managed service: the practical comparison
The table below describes typical arrangements, not universal product guarantees. Read each vendor’s feature list and service agreement because scanning intervals, response hours and remediation authority differ substantially.
| Question | Security plugin | Managed security service |
|---|---|---|
| What are you buying? | Software features, sometimes with a paid support tier. | An agreed operating process, usually supported by software and staff. |
| Who configures it? | Usually the owner, developer or agency. | May be the provider, subject to onboarding scope. |
| Who receives alerts? | Typically a configured email, dashboard or webhook. | Often a provider queue, sometimes also the customer. |
| Who investigates suspicious events? | Whoever is responsible for the site, unless support includes investigation. | The provider if investigation is explicitly included. |
| Who fixes vulnerable plugins? | The site team or its maintenance provider. | May be provider-led, coordinated or excluded. |
| Who handles a compromise? | Site owner or a separately hired specialist, unless cleanup is included. | Depends on incident-response and recovery terms. |
| Who maintains backups? | Not necessarily the plugin; often a separate backup solution. | May coordinate backups, but retention and restore testing must be specified. |
| What is the main trade-off? | More direct control and often lower software cost, but more internal effort. | Less internal operational burden, but more recurring cost and vendor dependence. |
Decision rule: Ask what happens at 2 a.m. when a critical alert arrives. If the only answer is “an email goes to an inbox,” you have a monitoring tool, not necessarily an operational response capability.
What a WordPress security plugin actually does
A security plugin runs inside WordPress, integrates with its configuration or connects to an external scanning or firewall service. Depending on the product, it can help restrict login attempts, prompt two-factor authentication, inspect file changes, compare files against known patterns, identify outdated components, log administrative activity, block selected requests or surface security warnings. These are useful controls when they are configured correctly and someone reviews their results.
Not all plugins have the same visibility. A plugin that operates inside WordPress may not see every server-level event, a malicious request stopped upstream, a compromised administrator’s laptop or an attacker’s activity in an unrelated hosting account. A cloud-based scanner can add an outside view, but external scans also have limits: they may miss malicious code that only executes for logged-in users or under particular conditions. A file-integrity alert can signal an authorized deployment just as easily as an unexpected modification; the finding needs context.
Plugins also introduce operational considerations. They require updates, may conflict with other plugins or caching layers, can create false positives, and may consume server resources during scans. Stacking multiple security plugins that perform the same firewall or login-lockout functions can complicate troubleshooting. The WordPress brute-force defense guidance recommends layered measures such as strong credentials, two-factor authentication and rate limiting, rather than treating a single plugin as a complete solution.
What a managed WordPress security service should add
At its most useful, managed security adds a repeatable human-led operating process around security controls. The provider may review alerts, classify severity, investigate suspicious changes, coordinate updates, recommend containment, oversee recovery and report the outcome. But the exact services are contractual. Some packages are essentially monitoring subscriptions. Others include hands-on remediation, incident response, backup restoration or coordination with the hosting company.
A credible service description should tell you which systems are monitored, how frequently checks occur, what triggers escalation, who is authorized to change production settings, which hours are staffed and what happens if an issue is outside the agreement. Ask whether the provider can examine hosting logs and CDN events, or only information visible inside the WordPress dashboard. Ask how access is granted, revoked and audited.
Managed security does not transfer every obligation to a vendor. The website owner still makes business-risk decisions, controls who may process customer data, approves disruptive changes where necessary and remains responsible for applicable legal or contractual duties. CISA’s guidance for managed service provider customers emphasizes clear service-level terms, incident-management responsibilities, remediation criteria and a shared-responsibility model.
Tell us about your website and the security concerns you want to address.
Talk to Defendoria ↗Where responsibility can fall through the cracks
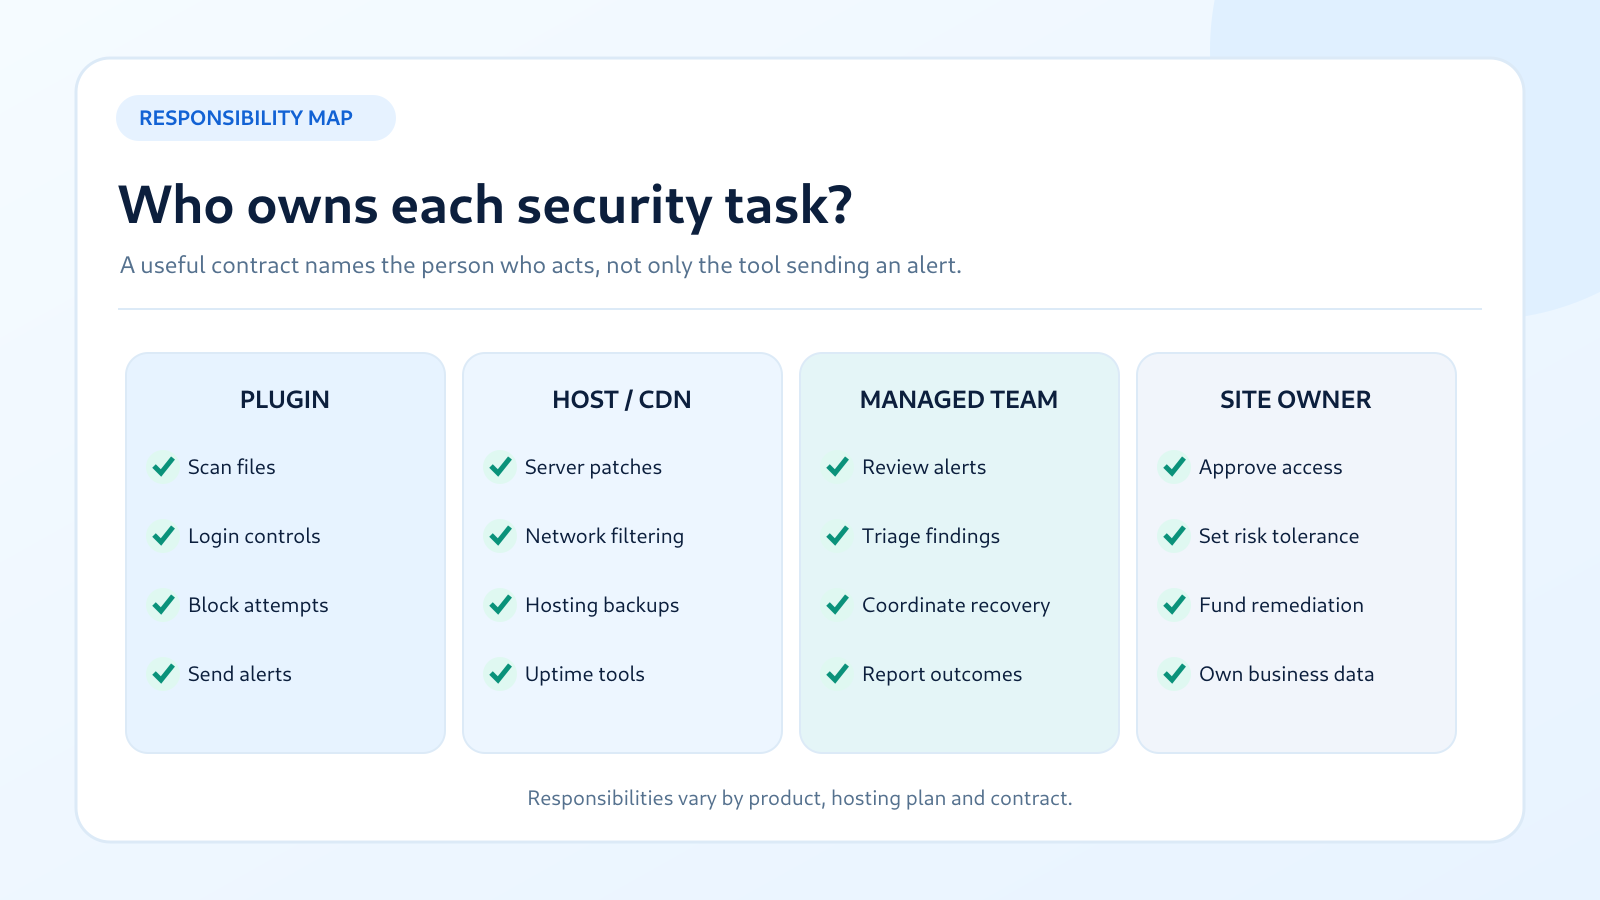
A WordPress installation commonly involves four parties: the site owner, the host, software vendors and any retained security or maintenance provider. Their responsibilities overlap, but they are not interchangeable. The host may maintain server infrastructure while the website team remains responsible for vulnerable third-party plugins. A security plugin may flag a suspicious file but have no authority to delete it. A managed provider may investigate an alert yet require the owner’s permission to take the site offline.
Write down who owns the following tasks: maintaining WordPress core, themes and plugins; enforcing multi-factor authentication; reviewing administrator accounts; configuring DNS and the CDN; inspecting logs; receiving alerts; approving emergency changes; retaining off-site backups; testing restoration; notifying affected stakeholders; and keeping evidence after an incident. Assign a primary owner and a backup owner to each high-impact task. An unassigned task is a gap even if a dashboard shows a green status indicator.
This also explains why “my host provides security” is not a complete answer. Hosting plans vary. Some provide managed WordPress updates and malware scanning, while others offer infrastructure protections only. The WordPress.com security documentation illustrates how a particular managed platform can bundle updates, scanning, backups and firewalls; those benefits should not be assumed for every hosting plan.
Five gaps a security plugin may leave unresolved
1. Alerts without an accountable responder
An alert that is never reviewed cannot reduce risk by itself. Notifications can be buried in a crowded mailbox, filtered as spam or sent to an employee who no longer works at the business. Confirm the alert destination, severity thresholds, backup contact and escalation procedure. Test a harmless notification and record whether it reaches the right person. Avoid generating real attacks simply to test an alert.
2. A scan without sufficient context
A scanner might identify an unfamiliar file or outdated component, but deciding whether it is malicious requires knowing the site’s normal state, recent deployments and the affected feature. Conversely, a clean scan does not prove that credentials, customer data or third-party integrations are safe. The OWASP Logging Cheat Sheet explains why application events and protected logs matter for investigation, not just web server logs.
3. Updates without compatibility planning
Installing a patch can close a known vulnerability, but it can also expose compatibility issues with a custom theme or payment extension. The answer is not to delay security fixes indefinitely. Maintain a tested backup, know which components are business-critical, use staging when practical and define a fast-track procedure for actively exploited vulnerabilities. See our guide to urgent WordPress security updates for a practical way to balance urgency and testing.
4. Backup creation without verified recovery
“Backups enabled” does not mean a usable restore point exists. A recovery plan needs the database and files, appropriate retention, access to credentials, a clean restoration environment and a test that confirms the website actually works afterward. A backup plugin might create archives but not provide an incident coordinator, or it might store copies in the same compromised account. Make sure at least one recoverable copy is appropriately isolated and protected from ordinary WordPress administrator access.
5. Blocking traffic without fixing the root cause
Firewalls and rate limits can reduce exposure, especially for automated requests, but they do not repair vulnerable application code or remove an unauthorized administrator. A web application firewall is one layer in a defense-in-depth program. The OWASP Application Security Verification Standard describes a broader set of controls for authentication, access, application behavior and verification. If an intrusion is suspected, preserve evidence and investigate the entry point instead of treating blocked requests as proof that the incident is resolved.
What an effective alert-to-response workflow looks like
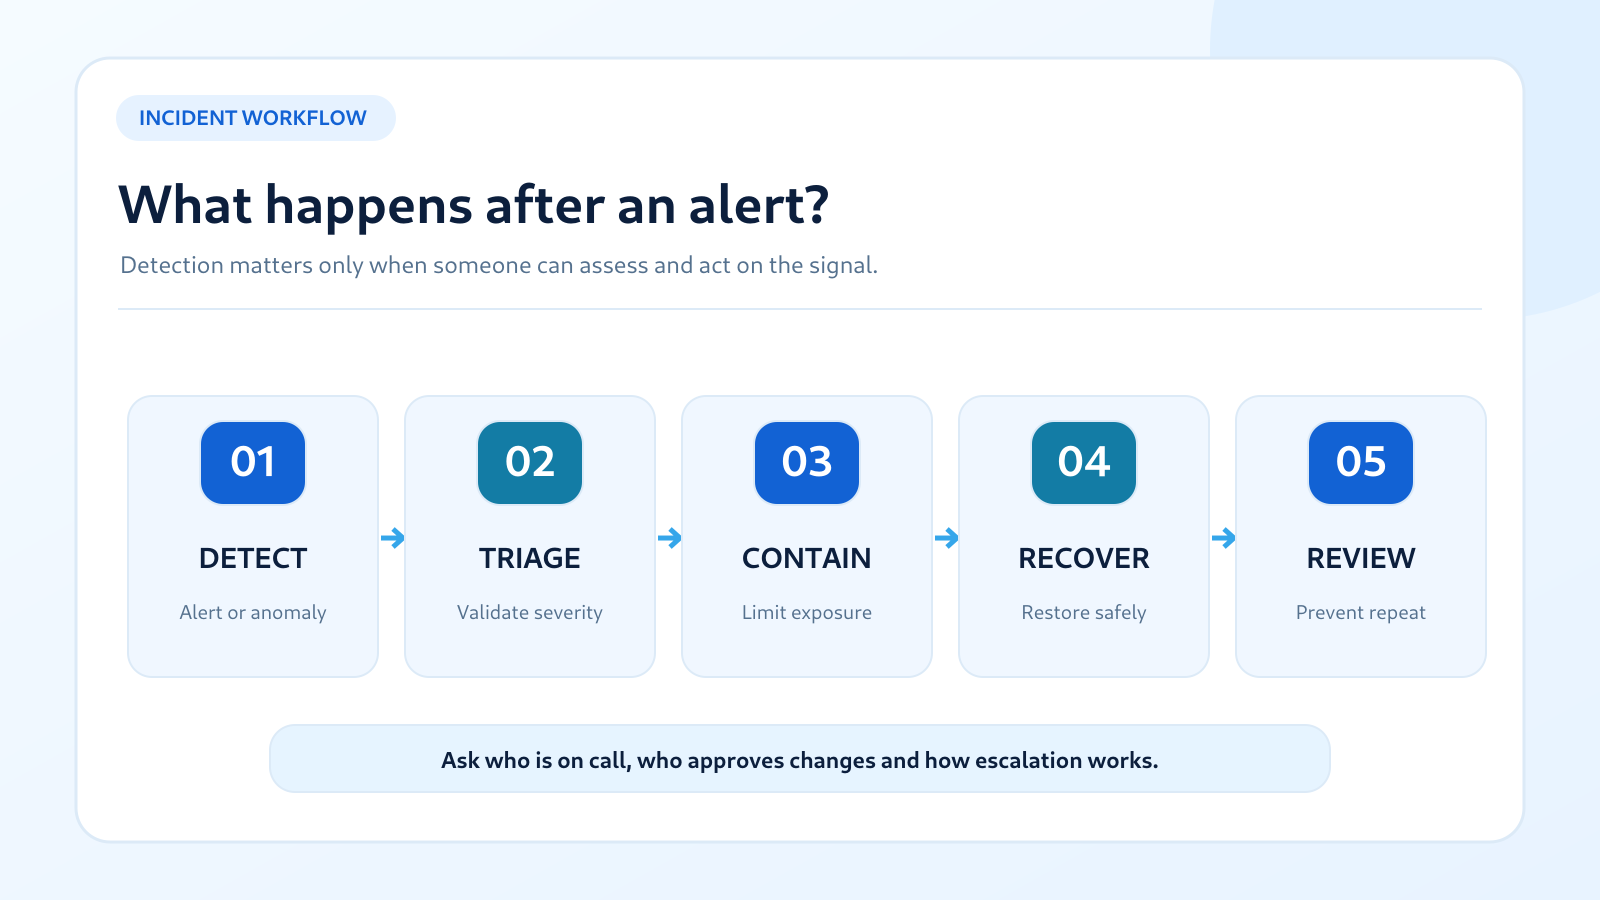
Imagine a security tool detects a new administrator account outside normal working hours. This is a hypothetical example, not a claim about a real Defendoria customer or incident. A plugin-only setup might send an email and record the event. Whether anyone responds depends on the site owner’s internal process. In a managed arrangement with investigation and response included, an assigned analyst might compare the event with approved user changes, review related login and audit logs, contact the owner, and recommend or execute an agreed containment step.
A disciplined workflow has five stages. Detect: collect a meaningful signal, such as a role change, unexpected file modification or suspicious login pattern. Triage: verify that the signal is credible and determine business impact. Contain: restrict the affected account or component only after considering evidence preservation and operational consequences. Recover: close the entry point, restore trusted components where appropriate and validate functionality. Review: document the timeline, root-cause evidence, lessons and control improvements.
Containment is not always as simple as deleting an account or removing a file. Premature deletion can erase evidence or break an integration. If the site may be actively compromised, coordinate with the host and qualified incident responders. For account-specific guidance, read how to investigate unauthorized WordPress administrators and what to do after a compromised admin account.
When a security plugin may be sufficient
A plugin-led approach can be reasonable for a relatively simple brochure site with limited personal data, few integrations and a knowledgeable owner or developer who reliably maintains it. It is especially practical when the hosting platform already supplies strong infrastructure protection, backups and meaningful security controls. “Sufficient” does not mean installing a plugin and forgetting it. Someone still needs to review alerts, manage updates, protect credentials and test recovery.
Before choosing that model, check that your team can answer basic operational questions: Who checks the site when the primary administrator is away? How quickly can a known critical vulnerability be patched? Who can restore the latest clean backup? Where are the hosting and domain credentials stored? If the answers are vague, the true cost of a low-cost plugin may include significant unattended risk.
When managed security becomes more valuable
Managed coverage can be more valuable when a website handles online orders, account logins, sensitive customer submissions, paid memberships or other revenue-critical functions. The same is true when an agency manages many client sites, the WordPress stack has extensive custom code, staff turnover complicates access control or the business has no dependable technical owner. Higher business impact makes response coordination and documented accountability more important.
It can also help when multiple systems are involved. A suspicious checkout redirect may involve WordPress, a payment plugin, a CDN rule, DNS or a compromised external script. Someone must coordinate the investigation across those layers. A provider with only WordPress dashboard access may not be able to resolve the entire problem, so access and escalation terms matter. For stores, our WooCommerce security service page explains the website-security areas worth reviewing; it does not replace a store-specific risk assessment.
Do not assume that paying for a managed plan means a guaranteed recovery time or uninterrupted service. Ask for written response objectives and the exclusions that could affect them. If a provider cannot state what happens after a confirmed incident, the word “managed” offers little practical clarity.
The hybrid option: software controls with targeted expert support
Many businesses do not need an all-or-nothing choice. A hybrid approach can combine a reputable security plugin, host-level controls, scheduled maintenance and a separate agreement for periodic security reviews or incident support. This can work well when the internal team handles routine updates but needs specialist help for complex findings. It also avoids paying twice for features already supplied by the host.
The risk is fragmentation: one vendor scans, another backs up, a third maintains the website, and no one owns the complete incident. A hybrid plan therefore needs one named coordinator, documented escalation contacts and an agreed handoff process. If you are comparing options, Defendoria’s managed website security page is a starting point for discussing scope, while a website security audit can help identify gaps before choosing a longer-term arrangement.
How to compare proposals without getting distracted by feature counts
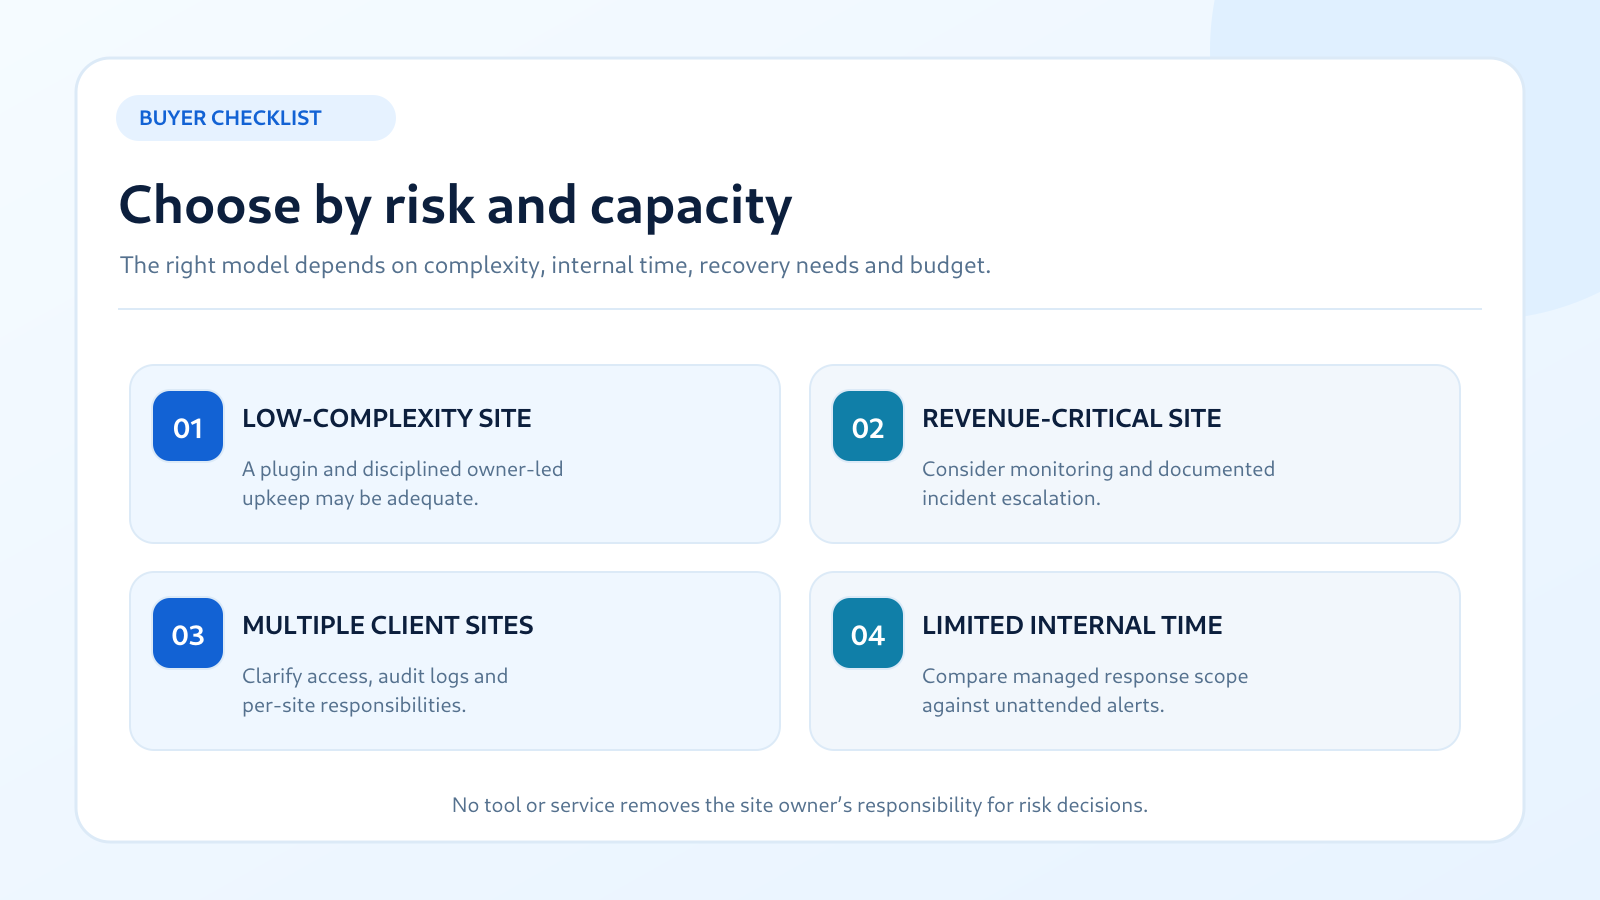
Two plans can both advertise “malware scanning,” “firewall protection” and “24/7 monitoring” while delivering very different outcomes. One might check files periodically and send automated email alerts. Another might include human triage, response coordination and a defined escalation path. Ask providers to demonstrate the workflow, not simply display a long list of checkmarks.
Questions to ask before signing
- What exactly is monitored? WordPress files, database, user activity, vulnerabilities, uptime, DNS, CDN and hosting logs may be separate scopes.
- How often are checks performed? Continuous telemetry, scheduled scanning and occasional manual reviews are different things.
- Who investigates alerts? Ask whether a person validates findings, during which hours and within what response objective.
- What remediation is included? Does the plan include removing malware, patching plugins, recovering from backups or only recommendations?
- What requires approval? Establish emergency authority for disabling accounts, changing DNS, blocking traffic or temporarily taking the site offline.
- How are backups handled? Confirm storage location, encryption, retention, restore testing and who pays for restoration work.
- What evidence will you receive? Request clear incident reports, change logs, findings, unresolved risks and a monthly summary appropriate to the plan.
- Who controls credentials and data? Prefer individual accounts, least privilege, multi-factor authentication and documented offboarding.
- What is excluded? Hosting outages, custom application vulnerabilities, third-party scripts, data-breach legal advice and emergency cleanup may not be covered.
- How can you leave? Clarify export of logs, configuration, backup copies and access revocation at contract end.
For a more technical review, map the proposed controls to the areas in OWASP ASVS. The goal is not to demand that every small site satisfy every advanced requirement, but to avoid treating a product feature list as evidence that all important risks have been addressed.
Cost: compare total ownership, not just subscription prices
A plugin may have a free tier, a recurring license or charges for premium scanning and support. Managed security usually adds recurring service fees, and some providers charge separately for onboarding, incident cleanup, emergency work, custom development or backup restoration. Actual pricing depends on the number of websites, traffic, complexity, data sensitivity, required response hours and service-level commitments. It would be misleading to publish a universal price without a defined scope.
For a fair comparison, calculate software subscriptions, staff hours spent reviewing alerts, patching and restoring, hosting features already included, external incident-support costs and the cost of business interruption. A small site with reliable in-house expertise may find a plugin-led model economical. A busy store with no technical staff may spend less operational effort with a properly scoped managed arrangement, although no provider can eliminate downtime or financial loss.
Be skeptical of absolute promises such as “100% hack-proof,” “instant cleanup in every case” or guaranteed search rankings. Security work reduces likelihood and impact; it cannot promise that every future attack will be prevented. Ask for measurable deliverables instead: reporting frequency, response objectives, backup-test evidence and remediation records.
Safe troubleshooting if you already have a plugin but feel unprotected
Start with an inventory, not an aggressive scan. Record the active plugin and version, license status, enabled modules, notification destinations, recent security alerts and last known successful backup. Compare the installed components with the official WordPress security guidance and your own maintenance policy. Check whether the host or CDN already provides overlapping firewall or malware-scanning functions.
Next, confirm that notifications work and that someone owns them. Review the WordPress administrator list against approved users; ensure privileged accounts use strong, unique credentials and appropriate multi-factor authentication. Examine recent updates and audit events for unexplained changes. Avoid making multiple disruptive changes at once, especially on a live store. Preserve evidence before removing suspicious files or accounts, and test restoration in a safe environment before relying on a backup.
If the website shows unexpected redirects, unknown administrators, injected content, payment-page anomalies or unexplained file changes, treat the issue as a possible incident rather than a plugin configuration problem. A security tool’s “clean” result does not override credible evidence of compromise. For practical next steps, use our safe WordPress malware removal guide and redirect investigation checklist. Seek qualified assistance if the site handles sensitive information or the evidence suggests active intrusion.
A sensible 30-day transition plan
Days 1–7: inventory and ownership. List WordPress administrators, installed plugins, external scripts, hosting and CDN accounts, backup locations and alert recipients. Confirm who approves security changes. Identify the highest-impact business functions, such as checkout, appointment booking or lead forms. Do not assume that an existing provider covers an area until the agreement says so.
Days 8–14: close basic gaps. Apply supported security updates with appropriate testing, enable strong authentication, remove unused accounts and software, verify off-site backups and review logging. Coordinate with the hosting provider before changing server or firewall settings. Record what changed and why so future alerts can be interpreted accurately.
Days 15–21: test the operating process. Send a harmless test notification, walk through a hypothetical account compromise, verify escalation contacts and perform a controlled backup restore test. The exercise should reveal missing credentials, uncertain ownership or impractical response expectations without creating an actual security incident.
Days 22–30: decide and document. Compare the time required for internal operation with the service coverage available. If you choose managed support, record the exact scope, response windows, permissions, data-handling terms, exclusions and exit plan. If you stay plugin-led, assign a named maintainer and review cadence. Revisit the decision when the site gains ecommerce, user accounts or new integrations.
Common misconceptions to avoid
“A paid plugin is the same as managed security.” Not necessarily. A paid license may add features or support but still leave investigation and remediation to the customer. Read the service terms.
“A managed service means someone is watching every event live.” Some plans use automated detection with business-hours review or on-call escalation. Monitoring frequency and human response hours are separate commitments.
“A firewall replaces patching.” No. It can block certain malicious requests, but vulnerable code and compromised credentials still require direct attention.
“The host is responsible for everything.” Hosts often protect infrastructure; application-level responsibilities depend on the hosting package and the owner’s configuration.
“A clean malware scan proves the site is safe.” No scan sees everything. Account compromise, external scripts, configuration errors and delayed malicious behavior can require different evidence.
“More security plugins always means better protection.” Overlapping controls can create performance, compatibility and alert-management problems. Select complementary layers with clear ownership.
Frequently asked questions
Can a WordPress security plugin remove malware automatically?
Some products offer automated cleanup for certain findings, but capabilities and reliability vary. Automatic deletion can also disrupt legitimate code if a detection is wrong. Confirm whether cleanup, investigation, validation and follow-up are included. If a compromise is suspected, preserve evidence and investigate how the attacker gained access.
Does managed WordPress hosting include managed website security?
Sometimes, but not always. Managed hosting may cover server maintenance, updates, backups and selected security controls without including application incident response or custom plugin remediation. Ask for a written responsibility matrix rather than relying on the word “managed.”
Is a security plugin enough for a WooCommerce store?
A plugin can be one useful layer, but an ecommerce site also needs secure payment integrations, controlled administrator access, patch management, reliable recovery, monitoring and appropriate handling of customer information. The required coverage depends on the store’s architecture and risk, not just the platform name.
Will a managed security service guarantee that my site cannot be hacked?
No responsible provider can guarantee that. A realistic service aims to reduce risk, detect problems, coordinate response and improve recovery readiness within its stated scope. Ask for evidence of processes and clear deliverables rather than absolute promises.
Do I need both a security plugin and a managed service?
Often a managed provider uses one or more tools, so you may not need to purchase a separate overlapping license. The right answer depends on the provider’s stack, hosting controls and any existing plugins. Avoid duplicate firewalls or scans without a clear reason.
Who should receive security alerts from WordPress?
Send alerts to a monitored destination owned by the responsible team, with a backup contact for absences. Separate urgent incidents from routine update notices. Test delivery and review escalation rules regularly, particularly after staffing or vendor changes.
How quickly should a provider respond to a security alert?
That depends on severity and the contracted service level. A suspicious privileged-account change may warrant urgent triage, while a low-risk informational scan result may be reviewed later. Define response objectives, coverage hours and what counts as acknowledgment, investigation and remediation.
Can I switch from a plugin-only setup to managed security later?
Yes. Start by documenting the current plugins, hosting, accounts, backups and unresolved findings. Give the new provider least-privilege access, verify overlapping controls and agree on the handoff. Remove old access only after confirming that monitoring, backups and emergency contacts remain functional.
Bottom line: buy the outcome and the accountability
For some websites, a reputable security plugin paired with careful maintenance is a sensible solution. For others, the real need is a dependable process for investigating alerts, coordinating fixes and recovering when something goes wrong. Compare the responsibilities, not just the logos or feature counts. Document who acts, what they can change, what evidence they provide and what remains the site owner’s responsibility.
If you want to clarify the gaps in your current setup, explore WordPress security support, managed website security or a structured website security audit. You can also contact Defendoria to discuss the site’s risk profile and the scope of assistance you need. No service should be selected without a clear understanding of what is and is not included.
Primary references and further reading
- WordPress Developer Resources — Hardening WordPress: official guidance on reducing application and hosting risk.
- WordPress Developer Resources — Brute Force Attacks: login protections and layered controls.
- CISA — Risk Considerations for Managed Service Provider Customers: contractual responsibilities and service expectations.
- OWASP — Logging Cheat Sheet: application event logging, alerting and secure log handling.
- OWASP — Application Security Verification Standard: a broader framework for verifying application security controls.
- WordPress.com — Keep Your WordPress Site Safe and Secure: an example of security responsibilities included with one managed hosting platform.
Editorial review: October 29, 2026. Features and service terms change; verify each provider’s current documentation and contract before purchasing. This guide is educational and is not a security assessment of any particular website.
This is general educational guidance, not a security assessment of a specific website. Obtain authorization before any technical testing.