“Something changed on our website.”
Unwanted redirects, strange popups, unknown users or unexpected file changes deserve careful triage, not random fixes.
From suspicious redirects and risky plugins to critical booking and checkout journeys, get a clear view of website-security priorities. Remote-first guidance and scoped security work for your website.
No passwords or security credentials are needed to enquire. Share your website, your concern and what an ideal outcome looks like. We will discuss an appropriate scope before any technical work begins.
Remote-first service enquiries for Buckeye, Arizona. Actual availability and terms are confirmed when we discuss the request.
Share a few details so we can discuss a suitable scope and next steps. No credentials needed.
\n
Businesses in Buckeye often depend on several moving parts: website platforms, customer forms, extensions, hosting and outside development teams. The difficult question is knowing which weakness deserves attention first.
Unwanted redirects, strange popups, unknown users or unexpected file changes deserve careful triage, not random fixes.
Plugins, theme dependencies and multiple administrators can make updates and access control difficult to coordinate.
Store owners need security decisions that consider critical purchase flows, external gateways and compatibility.
Without an agreed review cadence and escalation plan, important work can sit between teams.
Buckeye's official business-license guidance directs businesses to an online account portal, while its Development Services Department separately handles zoning, building and permitting questions for commercial and residential projects. These are government workflows, not services operated by Defendoria. For a Buckeye contractor or storefront preparing to open, the distinction matters: a public website may capture estimate requests, appointment details and uploaded plans, while city applications and invoices travel through their own channels. A practical website review can examine where these separate records meet inside a business's email, cloud storage and customer relationship tools. It should also help staff verify payment requests using known city contact channels instead of trusting an unexpected link. Defendoria can discuss a remotely scoped website assessment; this page does not imply an office or an assessment already performed in Buckeye.
Buckeye's Development Services materials describe reviews for commercial buildings and tenant improvements. A contractor's own site may accept project photographs, floor plans or quote requests before those official steps begin. Validate file types, restrict access to uploaded documents, set deletion periods and avoid emailing unrestricted attachment links to every subcontractor.
The city's business-license instructions direct applicants to a self-service portal and explain that an invoice follows review of a completed application. Businesses should clearly distinguish municipal transactions from their own deposits or online invoices. Publish verified contact details, train staff to confirm changed payment instructions out of band, and protect payment-related email accounts with phishing-resistant authentication.
When a Buckeye business adds a location or changes contractors, its website may gain new landing pages, enquiry forms and agency users. Maintain a current inventory of domain registration, DNS, hosting, backups and form integrations. Grant temporary vendor access only to the components they need, record who approves changes, and test a restore before a high-traffic campaign.
Examples describe website workflows, not findings from an assessment of local businesses. Any Defendoria work requires agreed scope and authorization.
Choose support around what is happening to your website today, not a generic list of features.
Review what is exposed, understand potential impact and organize a sensible order for improvements.
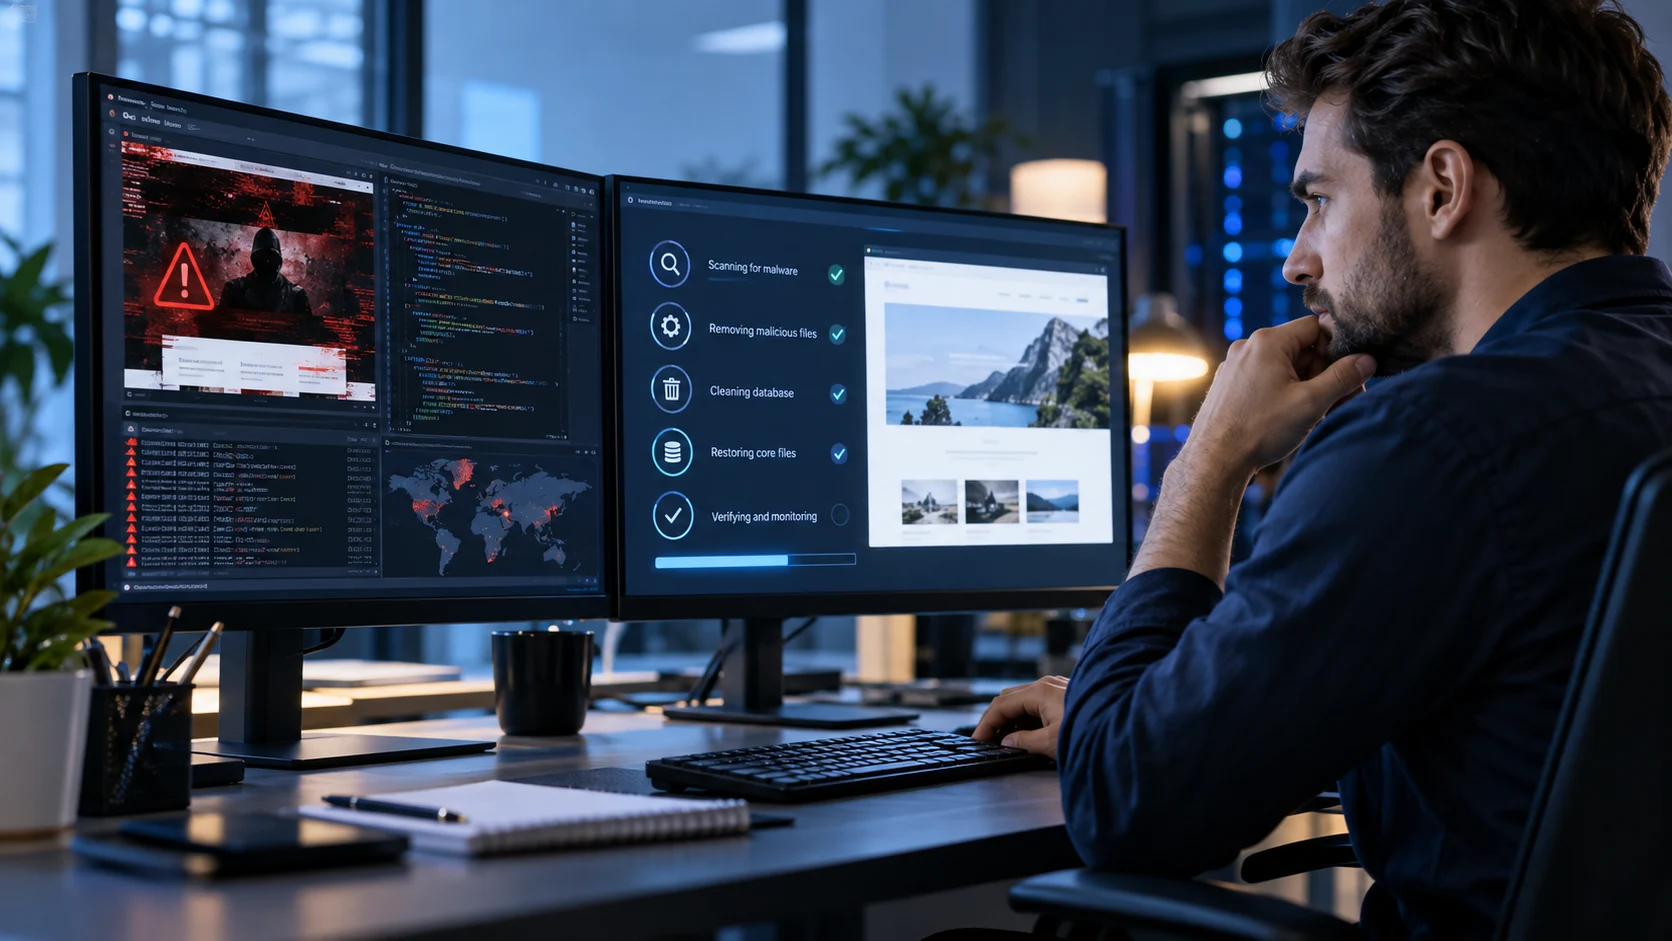
Understand suspicious behavior and agree on recovery priorities.
Plan safer updates, access rules and critical workflow checks.
Switch between common business scenarios to see where a conversation might start.
For teams that rely on their website for leads, contact forms, appointments or customer trust, an unclear security concern can interrupt normal work.
Share your platform, website URL, signs of a problem and the impact on your business. No passwords in the form.
Confirm ownership, systems in scope, agreed tasks, exclusions and how to obtain access safely.
Understand what a review could cover, which decisions matter and what needs your approval.
Technical work and deliverables follow the accepted proposal, with handover responsibilities made clear.
No automatic scans, invented guarantees or one-size-fits-all commitments.
For Buckeye-based companies, digital agencies and online stores, the practical security questions are often about who owns which systems, how decisions get approved, and what happens when something breaks.
Defendoria offers remote-first consultations. No local office or on-site personnel are claimed for this location.

Defendoria was founded by Dr. Syed M. Waqas Shah, PhD in Cyber Security. Our approach prioritizes clear communication, scoped assessment and practical decisions for the people responsible for a website.
Whether your site runs a store, takes bookings or represents a growing company, we start with your actual technology and responsibilities rather than one-size-fits-all promises.
Clear communication, authorization and scope matter just as much as the technical work.
You can request a remote-first consultation for your website. Service availability, scheduling and commercial terms are confirmed before any engagement.
Defendoria does not claim a physical office in this location. Website-security consultations are remote-first, and any technical work requires an agreed scope.
No. The inquiry is only a way to discuss a possible engagement. Technical access, scans and testing require separate, explicit authorization and a defined scope.
A website URL, your platform, a short description of the concern and how to contact you. Do not send passwords, payment details, access tokens or customer records in public forms.
No. Security depends on scope, site condition, dependencies and future threats. The agreed proposal should describe what will be reviewed or delivered, without promising risk-free operation.