
01
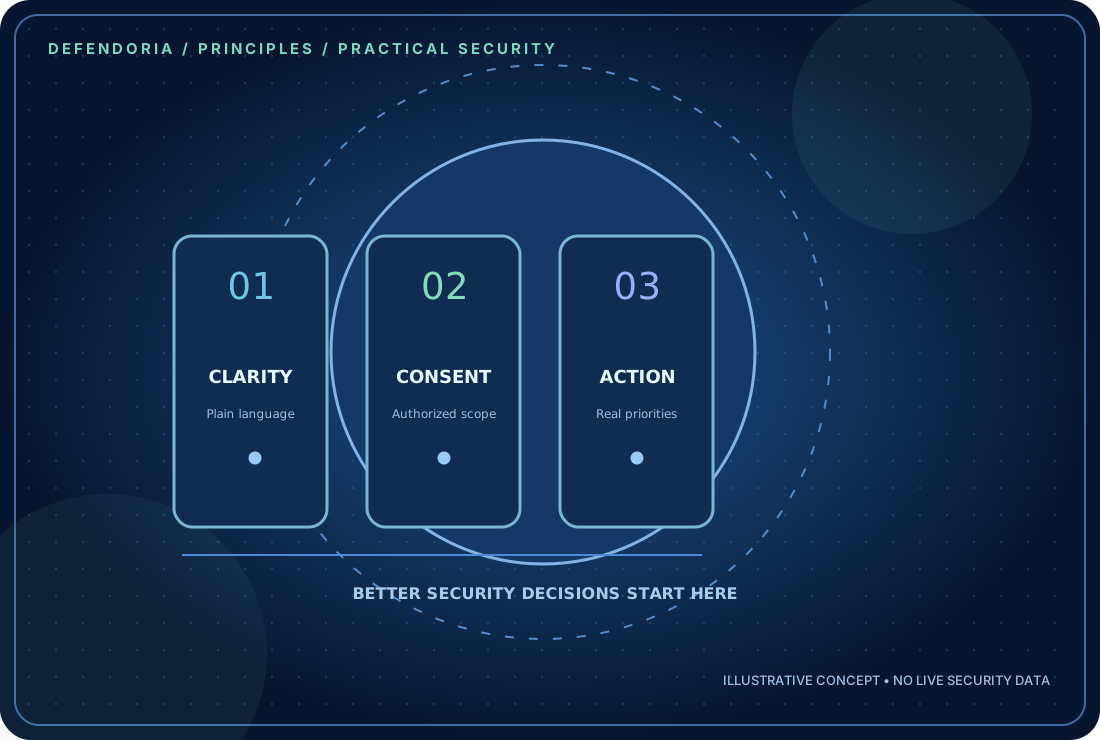
Explain the finding.
Security language should help owners make choices—not frighten them into purchasing work they don’t understand.
PLAIN LANGUAGE, REAL CONTEXTABOUT DEFENDORIA
We’re building Defendoria as a focused website-security service for businesses, online stores and agencies that need straightforward guidance and clearly scoped technical support.
WHAT DRIVES THE WORK
Defendoria is focused on helping people make informed website security decisions. That starts with being clear about what is known, what still needs investigation, and what a service includes.
Security language should help owners make choices—not frighten them into purchasing work they don’t understand.
PLAIN LANGUAGE, REAL CONTEXTA shared website URL is not permission to test it. Technical work needs an authorized, defined scope.
RESPECT THE BOUNDARIESRecommendations should connect findings to sensible ownership, priorities and practical action.
NO MAGIC SECURITY SCORESWe don’t claim every website is 100% safe, invent incident statistics, or use unverified customer endorsements. Our goal is work that can be explained and evaluated on its merits.
DEFENDORIA / LEADERSHIP / 01

FOUNDER / DEFENDORIA
Founder, Defendoria PhD in Cyber Security
The thinking behind Defendoria is simple: website owners deserve security guidance they can understand and act on, without the fear, jargon or inflated promises.
Dr. Shah brings a research-informed perspective to cybersecurity. His approach connects technical questions with the decisions that matter to businesses, including safeguarding website access, understanding software risks and planning sensible protection.
OUR POSITIONING
Defendoria is being built around a straightforward idea: business owners need website security advice that helps them make decisions, not another intimidating dashboard.
A storefront, lead-generation site and agency portfolio need different priorities.
We aim to make risks, testing boundaries and proposed actions understandable before technical work begins.
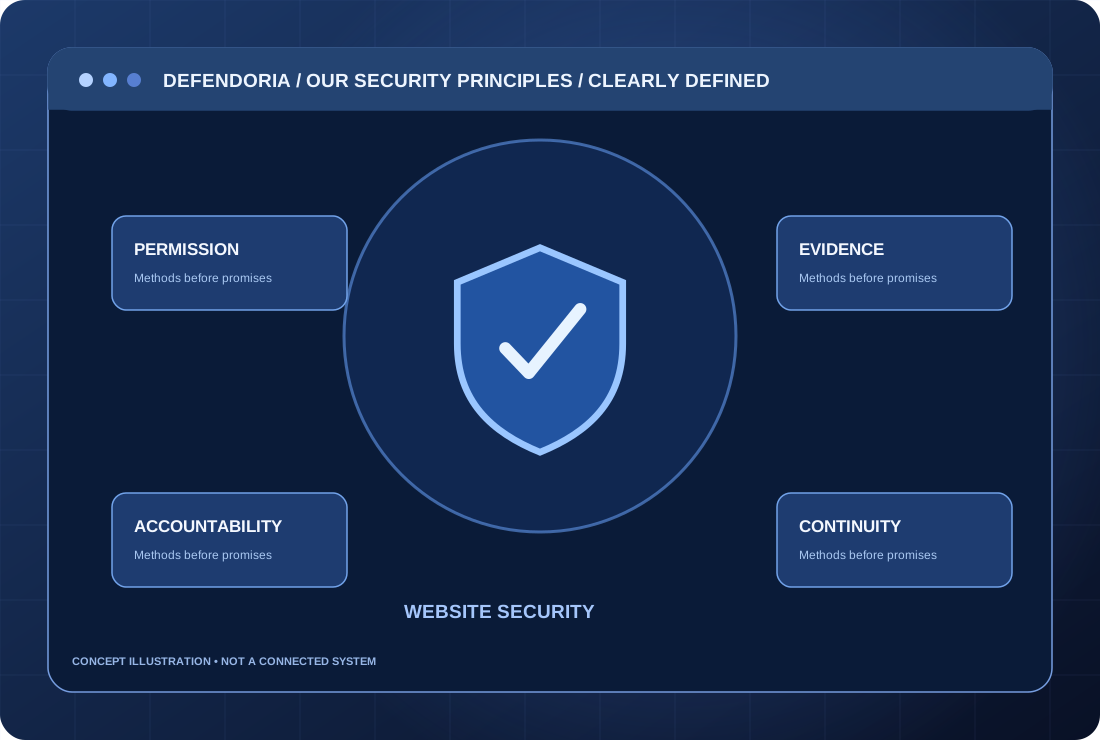
Document what was actually reviewed rather than treating an automated score as proof of security.
Security testing needs defined permission, target boundaries and safe handling of access.
Backups, restore dependencies and ownership matter just as much as preventing problems.
No audit, tool or provider can guarantee a website will never be compromised.
WHAT DEFINES THE APPROACH
Our public materials distinguish an illustrative design from a real security system, and an initial consultation from an authorized assessment. We believe that transparency should start before a contract.
OUR SERVICE FOCUS
We are developing dedicated services for the platforms and problems business website operators actually face.
Find and prioritize relevant risk with a clearly agreed scope.
Investigate suspicious changes and plan appropriate authorized remediation.
Build repeatable update, access and recovery practices.
Discuss how security services can complement client website work.
COMMON QUESTIONS
Every engagement is scoped to the website and authorization you provide.
The service focus is website security audits, malware recovery, WordPress and WooCommerce security, and ongoing protection.
No. We aim to help understand and reduce risk within a defined scope, not promise zero vulnerabilities.
No. Intrusive testing requires appropriate authorization, agreed targets and rules of engagement.
We will publish them when they can be substantiated. We do not use fabricated trust badges or testimonials.
GET STARTED
Tell us about the site you operate and the questions you want answered.
Share a few details so we can discuss a suitable scope and next steps. No credentials needed.